
The Biggest Cyber Attacks of 2023 (So far) Part 1
We’re already at the midway point of 2023 and so far there plenty of cyber incidents have hit the headlines. In this blog we take a look at some of the biggest cyber attacks of 2023 (so far).
Our Managed Detection and Response Services provide continuous monitoring from a team who’ll neutralise any breaches at speed...
Gain access to malware experts to quickly contain threats and reduce future exposure to attacks...
Integrity360 has been recognised as a Gartner Representative Vendor.
Many organisations are choosing CyberFire MDR to strengthen their defences. Discover how it can protect your business in our brochure.
Cyber attacks often seem faceless, but hidden behind the headlines of financial loss and technical details there are very real human stories.
In 2025, we’re witnessing a shift in how ransomware operates, who it targets, and the consequences of falling victim.
Stay ahead of the latest cybersecurity industry developments, advancements and threats, and understand how you can best protect your organisation.
Do you know what your company’s network vulnerabilities are? Businesses that invest in penetration testing do.
If your business handles credit card data, PCI DSS compliance isn’t optional—it’s critical. From retailers and e-commerce platforms to service providers and financial institutions, securing credit card data is critical to customer trust and preventing fraud.
Stay informed with the latest cybersecurity news with our weekly threat roundups.
Confused about cybersecurity? Our A-Z Glossary of terms can help you navigate this complicated industry.
For many small and mid-sized businesses, cybersecurity can feel overwhelming.
SOC 2 certification reflects Integrity360’s continued investment in strengthening cyber resilience for clients across highly regulated and high-risk industries.
Integrity360 has acquired leading Identity specialist CyberIAM, a well-established and highly respected cybersecurity Identity services company operating from the UK and South Africa.
 Under Attack?
Posts about:
We’re already at the midway point of 2023 and so far there plenty of cyber incidents have hit the headlines. In this blog we take a look at some of the biggest cyber attacks of 2023 (so far).
This week saw the release of a number of reports showing that payments to ransomware gangs fell in 2022. Our Incident response team offers some insight as to why that might be happening.
Our Incident Response Team has had another busy year as organisations fell victim to a wide range of cyber attacks and incidents. In this blog we cover the top 3 things our team thinks organisations need to consider as we head into 2023.
After years of increased threat complexity, most organisations simply don’t have the resources necessary to build an in-house cyber security strategy that’s equipped to deal with modern threats.
Panicked responses to a cyber-attack can often result in a race against risk that leads to rash and costly actions.
Modern enterprises don’t exist in a closed on-site ecosystem. Today’s organisations depend on an entire digital ecosystem of tools, provided by third party providers and cloud platforms, that ensure users can access the data they need to do their jobs no matter where they’re located.
Digital risks are all around modern organisations, from common phishing scams, to data exfiltration and leakage, copycat web pages and mobile applications, impersonating social media profiles, targeted Dark Web criminal activity, and exploitable vulnerabilities and misconfigurations.
However, many companies don’t have the visibility, expertise, or resources to manage and prioritise the mitigation of these threats.
As a result, many security teams are turning to managed threat intelligence and digital risk protection services to help them work alongside analysts with specialist skills they might lack, to optimise their ability to detect and respond to these external threats, and to keep up with the evolving threat landscape.
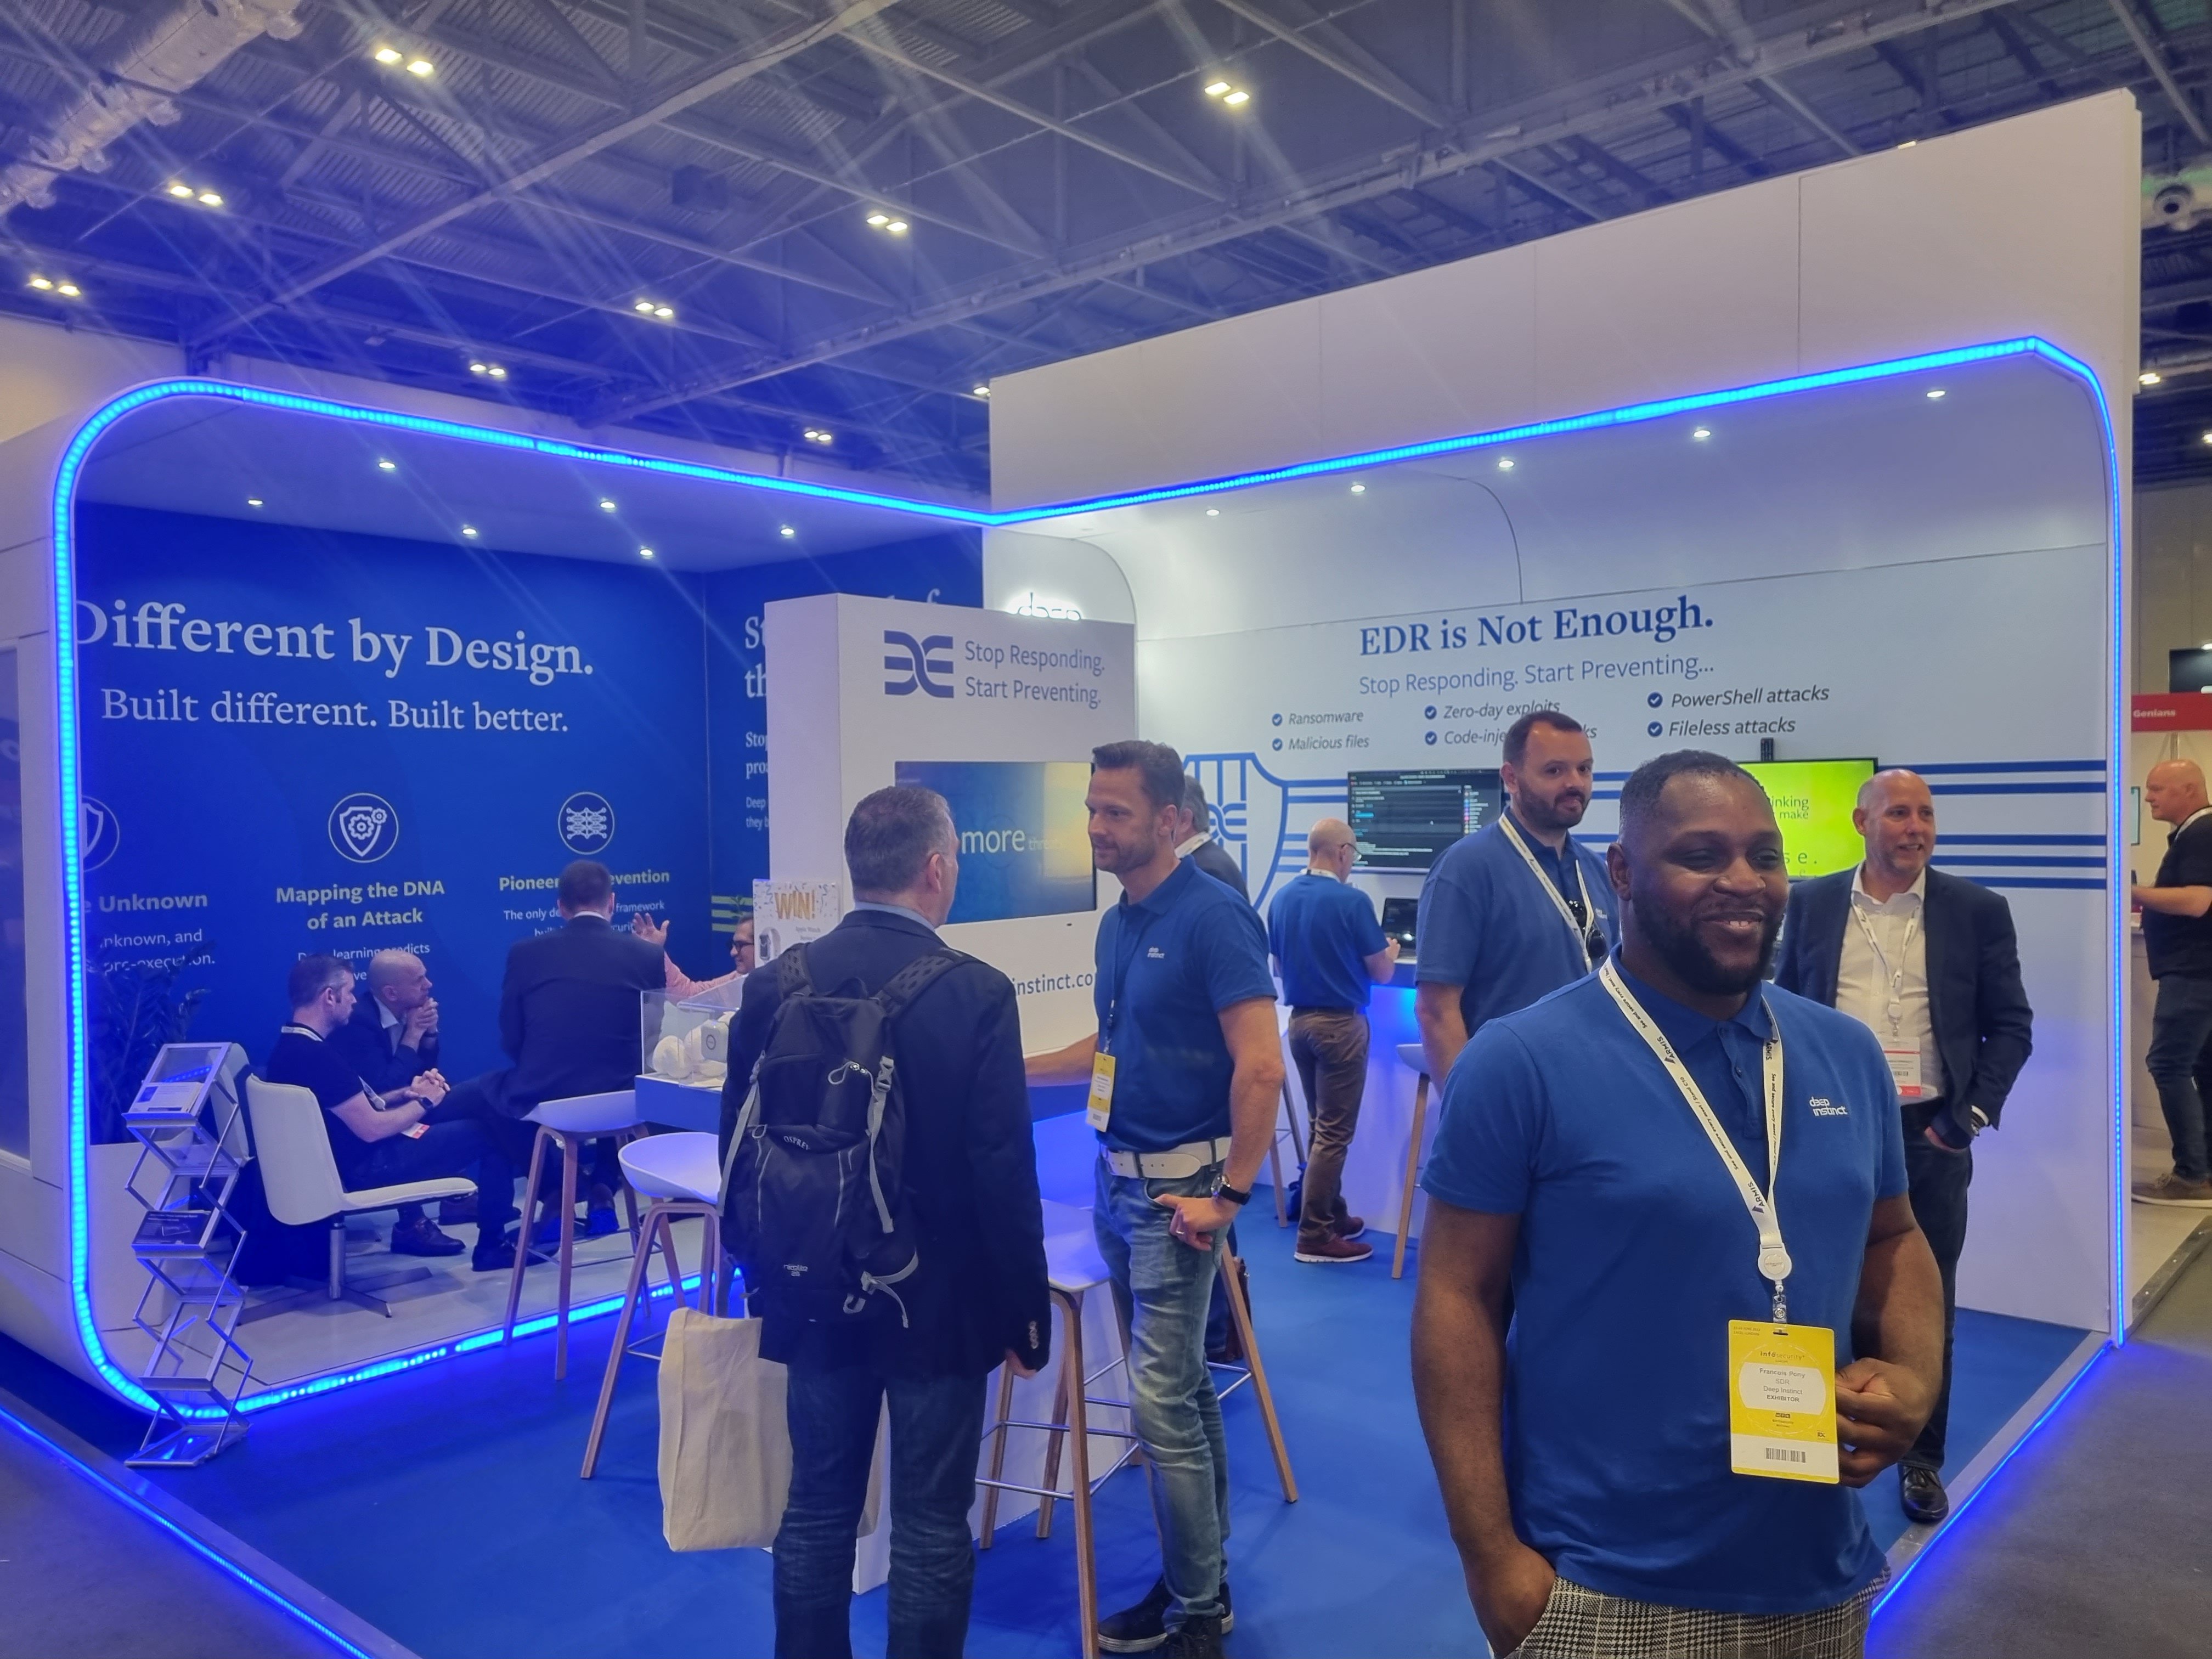
A couple of weeks ago, London’s ExCel brought together all corners of the information security industry for Europe’s largest gathering, InfoSec 2022 hosted from June 21st to 23rd, 2022. The event hosted a wealth of security vendor booths spread out across the exhibition halls, nearby hotels and even on a yacht, with day two finally bringing in the crowds of delegates.
We’re proud to share that Integrity360 has been shortlisted for two awards at the EU Cyber Awards. The awards provide the cyber industry with a valuable opportunity to celebrate some of the top providers, and movers and shakers in Europe, highlighting ground-breaking innovations and cyber solutions.
Wannacry ransomware first gained notoriety in 2017 after a global attack that was seen in over 150 countries and in excess of 300,000 devices. Some notable victims include the National Health Service (NHS) in the UK, Renault and FedEx. The feature that made this ransomware variant so successful was its worm-like properties, enabling it to spread across a computer network using the SMBv1 exploit EternalBlue. Wannacry encrypts user files and demands ransom be paid in bitcoin. The amounts were relatively small, usually between $300-$500 dollars, indicating the initial idea was less targeted and to get as many victims to pay as quickly as possible.
Although no threat actor took responsibility for the attacks, researchers found key identifiers in the code pointing towards the Lazurus group, an infamous North Korean cybercriminal organisation, and Korean timestamps in the ransomware metadata.
Integrity360 is delighted to announce that it been awarded 5 star Partner Status by Check Point Software Technologies, a leading provider of cybersecurity solutions globally. This makes the company the first indigenous Irish partner to achieve this status. It is also one of just eight Check Point partners in the UK market to be awarded the same.
Hamburg, Germany
Paris, France
Brussels, Belgium
Calgary, Canada
Chester, United Kingdom