

PCI DSS 4.0.1: What changed and what you need to know in 2026
Updated 18/8/26
Our Managed Detection and Response Services provide continuous monitoring from a team who’ll neutralise any breaches at speed...
Gain access to malware experts to quickly contain threats and reduce future exposure to attacks...
Integrity360 has been recognised as a Gartner Representative Vendor.
Many organisations are choosing CyberFire MDR to strengthen their defences. Discover how it can protect your business in our brochure.
Cyber attacks often seem faceless, but hidden behind the headlines of financial loss and technical details there are very real human stories.
In 2025, we’re witnessing a shift in how ransomware operates, who it targets, and the consequences of falling victim.
Stay ahead of the latest cybersecurity industry developments, advancements and threats, and understand how you can best protect your organisation.
Do you know what your company’s network vulnerabilities are? Businesses that invest in penetration testing do.
If your business handles credit card data, PCI DSS compliance isn’t optional—it’s critical. From retailers and e-commerce platforms to service providers and financial institutions, securing credit card data is critical to customer trust and preventing fraud.
Stay informed with the latest cybersecurity news with our weekly threat roundups.
Confused about cybersecurity? Our A-Z Glossary of terms can help you navigate this complicated industry.
For many small and mid-sized businesses, cybersecurity can feel overwhelming.
SOC 2 certification reflects Integrity360’s continued investment in strengthening cyber resilience for clients across highly regulated and high-risk industries.
Integrity360 has acquired leading Identity specialist CyberIAM, a well-established and highly respected cybersecurity Identity services company operating from the UK and South Africa.
 Under Attack?
Posts by:
Updated 18/8/26
The secure handling of payment card data is imperative. The Payment Card Industry Data Security Standard (PCI DSS) first established in 2005 and now in its 4.0 version, serves as an industry baseline guide to ensure that businesses handle Cardholder Data with utmost security. But what exactly is PCI DSS, and why is compliance so important? Are financial penalties, reputational damage, and legal liability consequences of non-compliance? Here's an in-depth look at this standard and how it fits into your company’s cyber security strategy.
Enterprise Times talked with Richard Ford, Chief Technology Officer at Integrity360, about Managed Detection and Response. In the past, tools have been sold based on fear and the need to have multiple overlapping tools to plug gaps. But that has come at a price of complexity which, in itself, leads to gaps and mistakes. Listen to Richard's insights in the podcast below.

The European Union Agency for Cybersecurity (ENISA) recently released its report on the cyber threat landscape for the healthcare sector and it didn’t make for pretty reading.
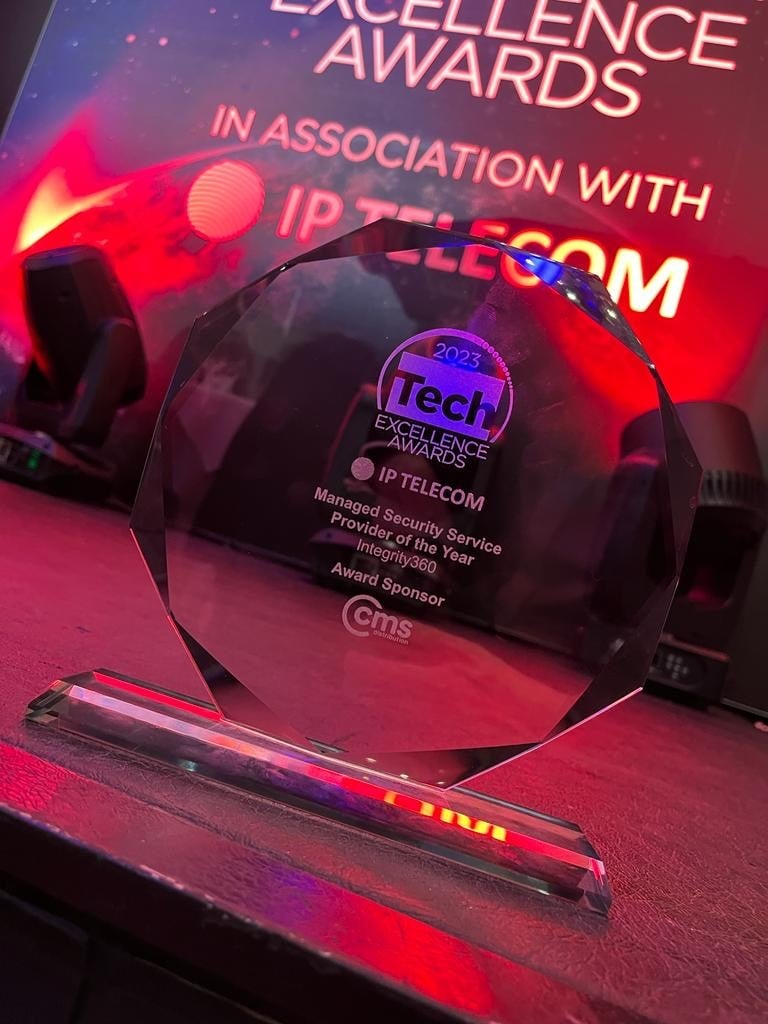
Dublin, 26th May 2023 – Integrity360,Ireland’s largest cyber security services specialist, today announces that it been crowned Managed Security Services Provider of the Year at the 2023 Tech Excellence Awards.
London, 3rd April 2023 – Integrity360, one of the fastest-growing and largest independent pure-play cyber security specialists in the UK and Ireland, today announced that it has been named as a Representative Vendor* in the 2023 Gartner Market Guide for Managed Detection and Response (MDR) Services.
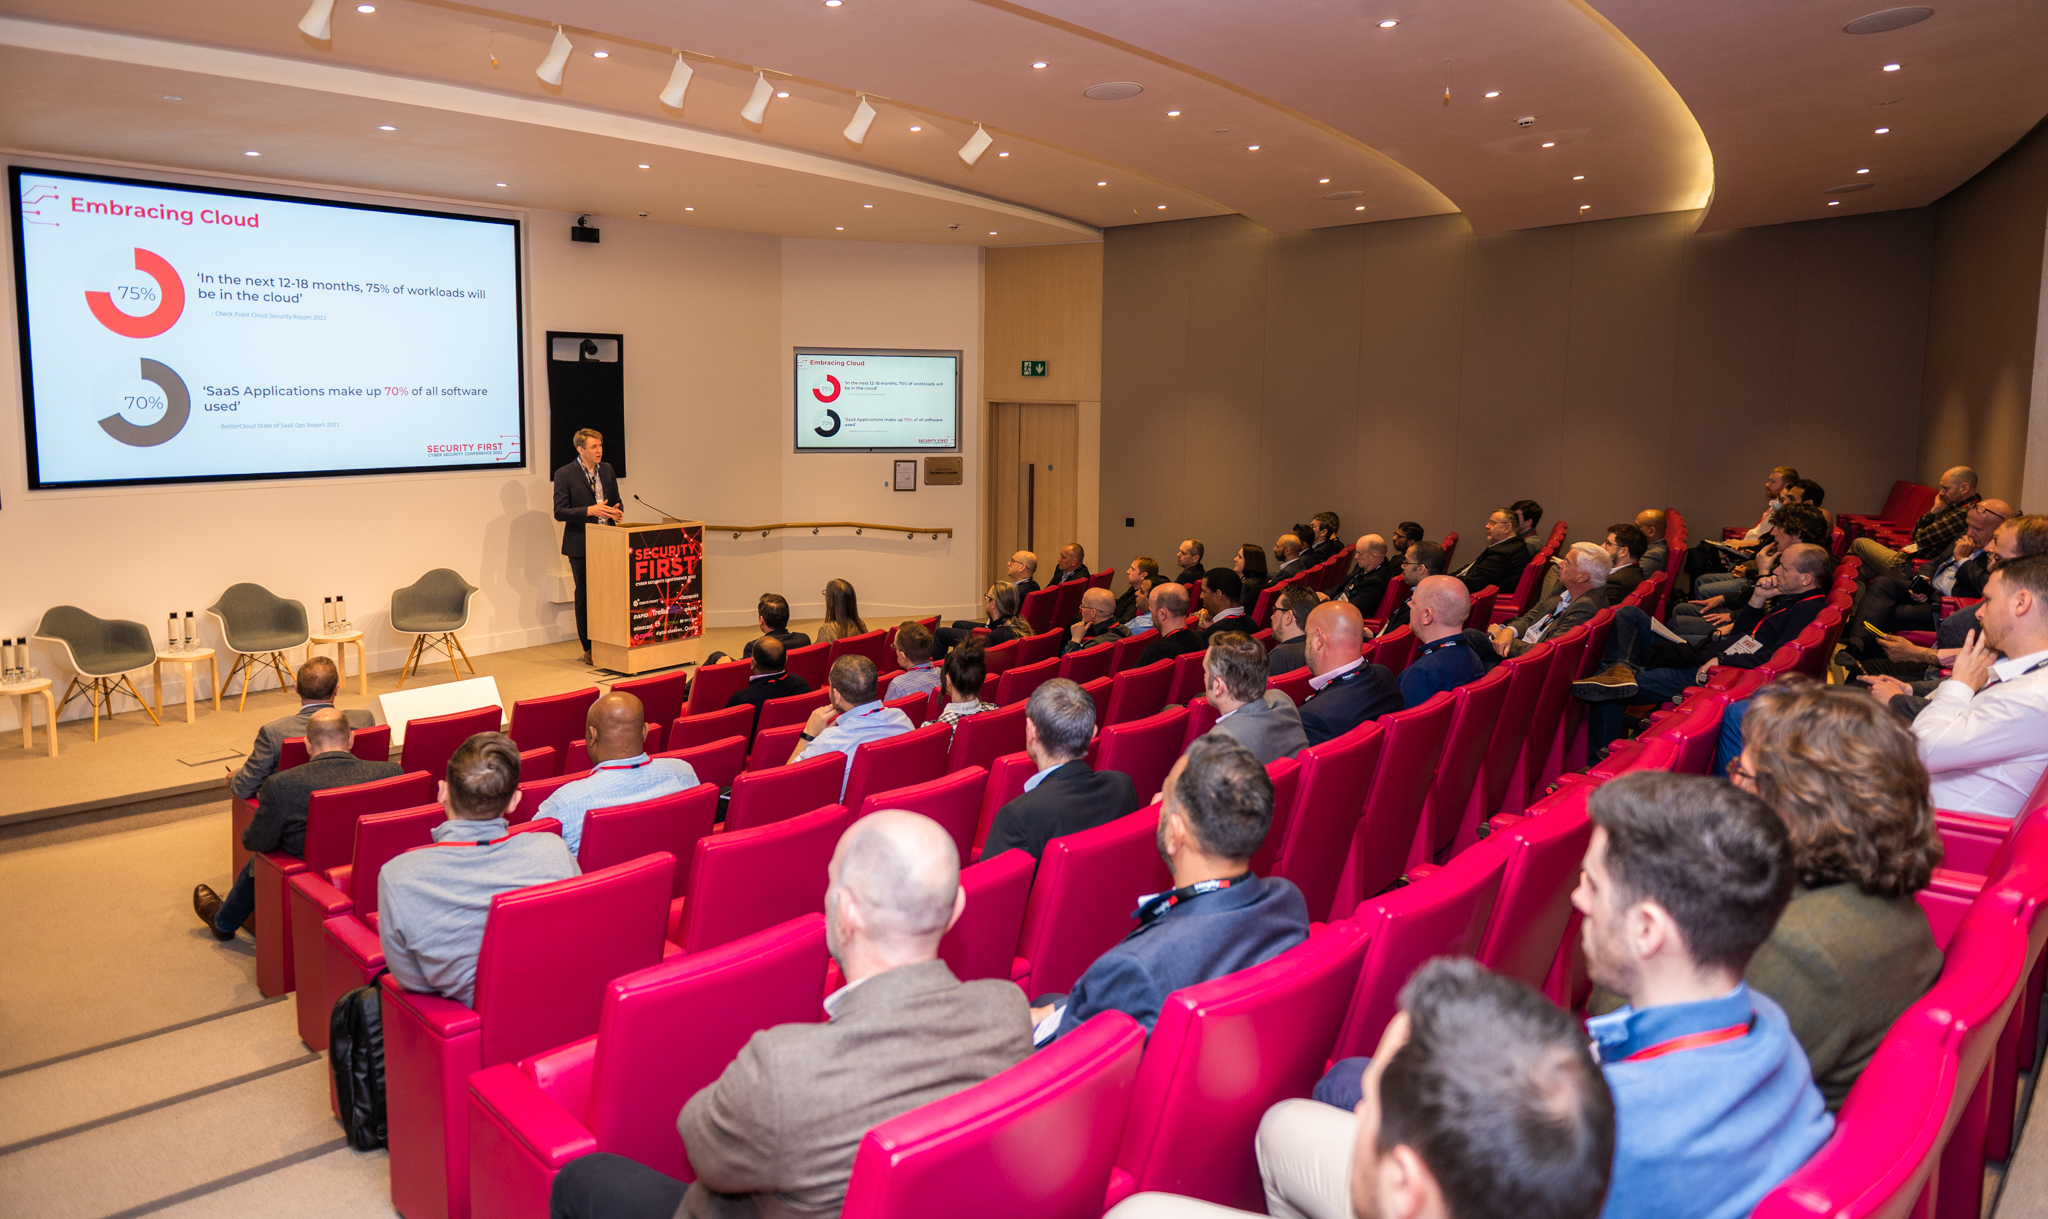
We’re delighted to announce that the keynote speaker for our upcoming Security First Conferences in London (March 22nd) and Dublin (April 27th) will be cybercrime investigative journalist and author Geoff White.
With the complexity of cyber threats increasing across the board, general approaches to cyber security aren’t enough to protect your organisation. You need cyber security that can address each threat on a case-by-case basis.
More and more organisations are realising the benefits of achieving compliance with an international security standard, and more specifically the ISO27001.It’s a standard that was first released in October 2005sowhy is thisstill relevant today?– It continues to be largely drivenby client requirements, the desire for a competitive advantage or simply wanting to ensure the most robust security practices for the company and its stakeholders.
The Covid-19 pandemic changed the way we work in the UK and Ireland forever. As companies experimented with remote working to maintain productivity, many employees became accustomed to the idea of working from home and enjoying a greater work-life balance.

How can you maximise your return on security spend? What happens to security now, post pandemic? Do you understand the real impacts a ransomware attack would have on your business? Our security experts and partners answered these questions and more at our Security First Roadshow events.
After years of increased threat complexity, most organisations simply don’t have the resources necessary to build an in-house cyber security strategy that’s equipped to deal with modern threats.
Hamburg, Germany
Paris, France
Brussels, Belgium
Calgary, Canada
Chester, United Kingdom




